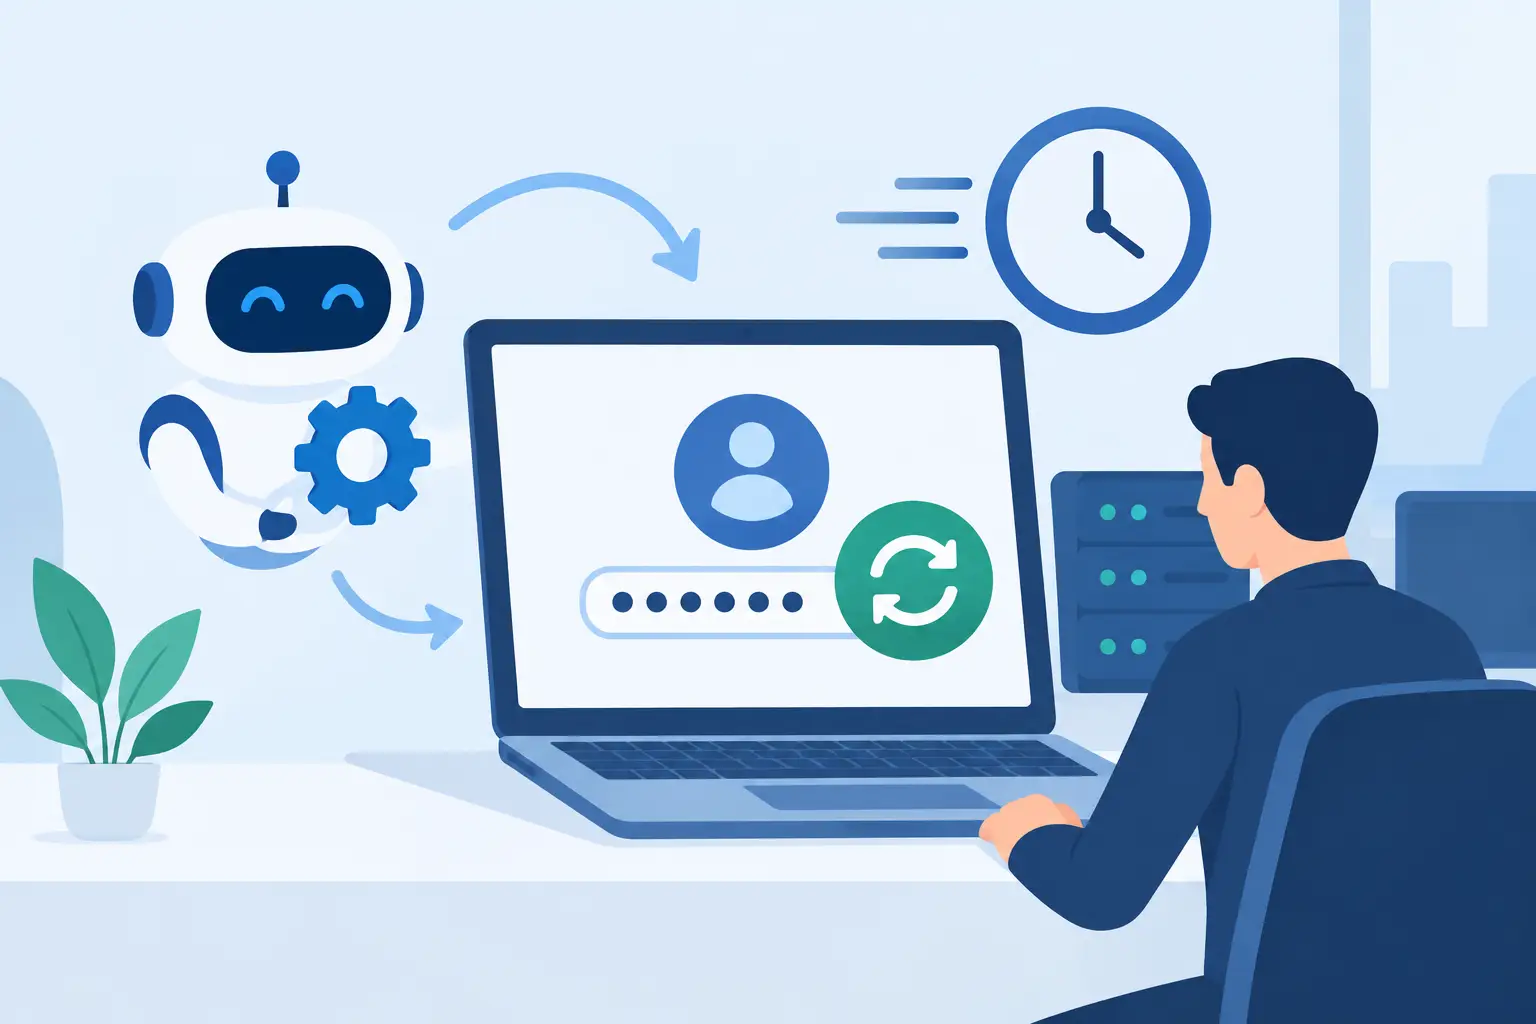
A locked account can stop a workday faster than a server outage. A staff member cannot open email, a field supervisor cannot access job files, and someone in finance is waiting on a shared system before payroll can move forward. An automated password reset tool gives employees a secure way to resolve routine access problems without waiting in an IT queue.
That sounds like a small improvement until you look at the interruptions behind it. Password resets often arrive first thing in the morning, after a weekend, or minutes before a deadline. Each request may take only a few minutes to handle, but it pulls technicians, office managers, and employees away from work that actually needs their judgment.
Why password resets create bigger operational problems
Most businesses do not struggle because they lack a way to change passwords. They struggle because the process is inconsistent. An employee sends an email to a shared inbox, calls whoever answers the phone, or waits until a manager is available to confirm their identity. Meanwhile, the employee is stuck and the request is easy to miss.
For a small or mid-sized organization, the impact spreads quickly. One person loses 20 minutes of productive time. Another person stops to help. IT has to verify identity, reset the account, document the request, and hope the employee can sign in again. If the reset applies to only one system while the real issue is a device, network connection, expired account, or multi-factor authentication prompt, the same person may call back five minutes later.
A useful automated password reset tool should reduce those handoffs, not merely move them into a portal nobody wants to use. Employees need a clear path in plain language. IT needs confidence that the person making the request is who they say they are. Managers need visibility without becoming part of every routine approval.
What an automated password reset tool should do
The right setup starts with the systems your staff already use. In many Windows-based workplaces, that means connecting password reset actions to the identity platform that controls workstation logins, email, cloud applications, and permission groups. The goal is to solve the access issue once, then let the new credentials follow the employee where they need to work.
Self-service matters, but it cannot mean self-service without controls. A well-designed process verifies the employee through approved methods, such as a registered authentication app, security prompt, recovery contact, or a defined combination of identity checks. The exact method depends on the risk level of the account and the tools already in place.
It should also explain what is happening. Staff should know whether their account has been unlocked, whether a password was changed, and what to do if their computer still will not accept the new password. A short, direct message can prevent a second ticket and a frustrated call to the office.
For routine cases, automation can complete the task immediately. For anything unusual, it should create a ticket with the right context and send it to a real person. That includes repeated lockouts, failed identity verification, access requests involving sensitive accounts, and situations where an employee may be leaving the organization.
Password reset is not the same as account recovery
This distinction matters. A password reset handles a known user who cannot sign in. Account recovery may involve a lost device, a changed phone number, suspicious activity, an unknown login location, or someone who no longer has access to their verification method.
Trying to automate every recovery scenario creates risk. A finance administrator or executive assistant with access to sensitive records should not be able to regain control of an account through a weak fallback process. In these cases, the best system pauses the request, records what happened, and sends it to an authorized technician or manager for a proper check.
Build the workflow around real workplace situations
Before choosing or configuring a tool, look at the password requests you already receive. The pattern tells you where automation will help and where human review remains necessary.
A practical workflow usually needs to cover five situations:
- An employee forgot a password but still has their approved verification method.
- An employee is locked out after too many failed sign-in attempts.
- An employee changed a password but a laptop, phone, or mapped drive still needs to reconnect.
- An employee cannot complete identity verification because a device was lost or replaced.
- A request appears unusual and needs human review before any account changes are made.
The first two can often be handled quickly and safely. The third may need guided troubleshooting, such as reconnecting Wi-Fi, updating saved credentials, or waiting for a device to sync. The last two should be escalated, with the details already captured so employees do not have to repeat their story.
This is where a conversational assistant can be more useful than a generic reset page. Instead of asking staff to guess which form applies, they can state the problem: “I changed my password and Outlook still will not open,” or “My phone is gone and I cannot get into email.” The assistant can ask the next sensible question, start the allowed workflow, and bring in a technician when the situation crosses the line from routine to sensitive.
Security controls that should not be skipped
Password automation should reduce risk, not make access easier for the wrong person. The controls should be proportionate to the systems involved, but a few principles apply almost everywhere.
First, verify identity using more than information that could be found in an email signature, social media profile, or company directory. Second, log each request, verification step, reset action, and escalation. When someone asks what happened to an account, there should be a record rather than a guess.
Third, apply different rules to different roles. A warehouse employee, an office coordinator, a system administrator, and a payroll manager should not necessarily follow the same recovery path. Privileged accounts deserve tighter controls, shorter response windows, and direct review.
Finally, watch for patterns. Frequent password resets can point to confusing requirements, an application that is storing an old password, staff sharing credentials, or a device that is repeatedly trying to connect with outdated information. Automation gives you better data, but someone still needs to act on it.
Measure the result in time returned to the business
The value is not just fewer tickets. Track how long employees are locked out, how many requests are resolved without technician involvement, how many are escalated, and how often the same person or device causes repeat issues.
Those numbers help you see whether the process is actually working. If self-service completion is high but repeat lockouts are also high, the reset tool may be treating symptoms instead of fixing a configuration problem. If technicians are still handling most requests, identity verification may be too difficult or the instructions may be unclear.
For many organizations, the first benefit is after-hours coverage. An employee working an early shift or preparing for a client meeting does not need to wait for the office to open just to regain access. The second benefit is focus. Your IT team can spend less time performing predictable account tasks and more time solving printer failures, application problems, security concerns, and the projects that keep operations moving.
Make automation part of accountable support
A password reset process should not leave staff alone when it fails. The technology needs a defined escalation path, clear ownership, and people who understand your environment. Nothing off the shelf will know your approval rules, shared devices, application dependencies, or which accounts need special handling without being configured around them.
Meet Gwen can handle the front end of routine IT requests in ordinary language, guide employees through approved steps, and pass complex cases to a technician with the context already collected. That means less back-and-forth for staff and fewer routine interruptions for the people responsible for keeping systems running.
Start with the requests that steal time every week. Map the safe path, identify the exceptions, and make sure a real person is ready for the cases automation should not touch. A good password reset experience does not make IT disappear. It makes help available at the right level, at the moment work would otherwise stop.